Home>Software and Apps>Troubleshooting a VPN That Connects but Loads Nothing
Software and Apps
Troubleshooting a VPN That Connects but Loads Nothing
Modified: 28 October 2026
Table of Contents
Your VPN says it's connected, but every website times out or loads a blank page. The fix is almost always a DNS leak or a protocol mismatch. Here is how to find which one and stop it.

Why Your VPN Connects but Loads Nothing
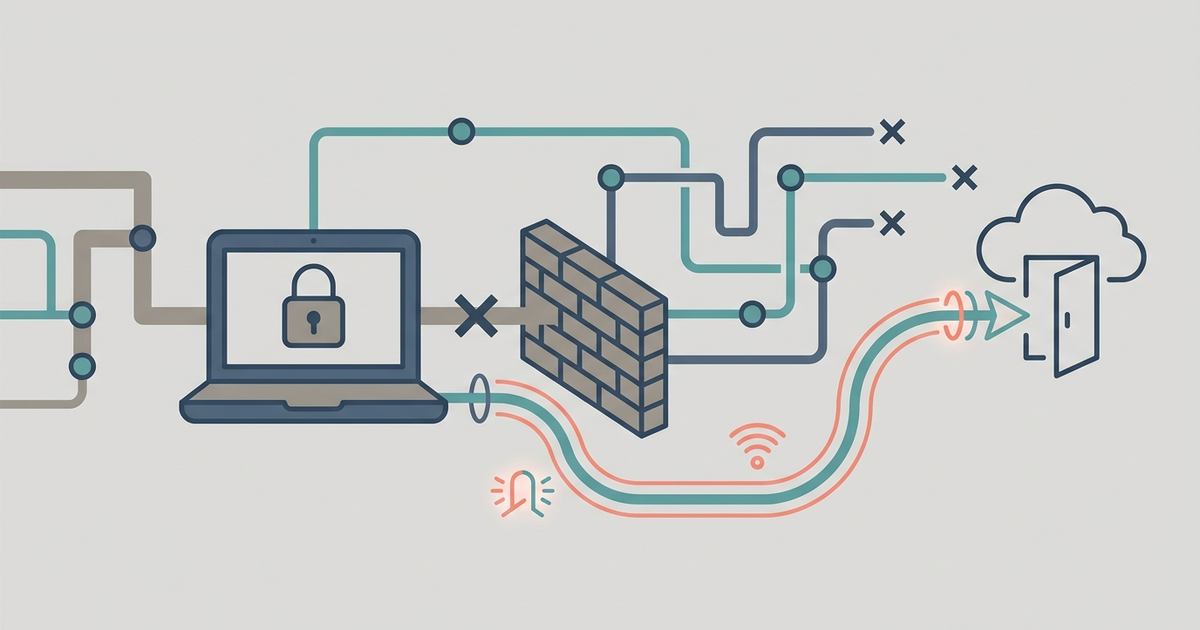
A successful VPN connection means your device has a secure tunnel to the VPN server. But loading a website requires DNS resolution — turning a domain name like google.com into an IP address. If that DNS request leaks outside the tunnel, or if your VPN's DNS servers are blocked, pages fail. IPv6 traffic can also bypass your VPN entirely. Some ISP routers or firewalls deliberately throttle VPN protocols. Test each possibility in order.
Check for a DNS Leak First
Open a browser and go to dnsleaktest.com or ipleak.net. With your VPN connected, run the standard test. The page will show the IP address and DNS servers it detects. If you see your real ISP's DNS servers — or any IP that belongs to your home internet provider — you have a DNS leak. That leak means your browser is asking your ISP where websites live, and your ISP can block or redirect those requests. If the test shows only the VPN server's IP and DNS, move on to the next step.
Force Your VPN to Use Its Own DNS Servers
Even when your VPN app claims to manage DNS, your operating system can override it. Force the VPN's DNS servers manually.
In NordVPN (around $3.29/month on the 2-year plan)
- Open Settings > Advanced > Custom DNS.
- Toggle it on and enter 103.86.96.100 and 103.86.99.100 (Nord's own servers).
- Reconnect the VPN.
In ExpressVPN ($6.67/month on the 1-year plan)
- Go to Options > Advanced > DNS Settings.
- Choose "Force DNS" and enter 1.1.1.1 or 9.9.9.9 as a fallback.
- ExpressVPN does not expose its internal DNS servers, so using Cloudflare or Quad9 is the next best option.
In Mullvad (€5/month)
- Open Settings > DNS Content > Custom.
- Enter 194.242.2.2 and 194.242.2.3 (Mullvad's ad-blocking DNS).
- Click Save and reconnect.
After forcing DNS, run the leak test again. If the leak is gone, you are fixed. If it persists, proceed.
Switch to a Different VPN Protocol
The protocol your VPN uses changes how it handles DNS and how easily your ISP can interfere. When pages won't load, which protocol you try first matters.
WireGuard is the modern default. It is fast and uses encrypted UDP packets that look like random noise. Most ISPs cannot easily block it. Try WireGuard first. It is available in NordVPN, ExpressVPN, and Mullvad. On NordVPN, it is called NordLynx. On ExpressVPN, it is the Lightway protocol. On Mullvad, it is the default.
OpenVPN is older and runs over TCP on port 443, which mimics HTTPS traffic. If WireGuard fails, switch to OpenVPN TCP. It is slower but more likely to bypass aggressive ISP filtering. ExpressVPN and Mullvad let you select OpenVPN TCP explicitly. NordVPN offers it under "OpenVPN (TCP)".
IKEv2 uses UDP port 500 and is often blocked by corporate or hotel firewalls. It is the least reliable for general browsing. Only use IKEv2 if the other two fail entirely. IKEv2 is available in NordVPN and ExpressVPN. Mullvad does not support it.
Start with WireGuard, then OpenVPN TCP, then IKEv2 as a last resort.
Disable IPv6 on Your Device
Many VPN apps do not route IPv6 traffic through the tunnel. Your device can have a working IPv4 connection through the VPN while IPv6 requests leak straight to your ISP. Disable IPv6 to force everything over IPv4.
On Windows 11
- Open Control Panel > Network and Internet > Network and Sharing Center > Change adapter settings.
- Right-click your active network adapter > Properties.
- Uncheck Internet Protocol Version 6 (TCP/IPv6).
- Click OK. Reconnect your VPN.
On macOS Ventura
- Open System Settings > Network.
- Select your active network service (Wi-Fi or Ethernet) > Details.
- Click TCP/IP. Change "Configure IPv6" to Off.
- Click OK. Reconnect your VPN.
On Android 13
- Open Settings > Connections > Mobile networks (or Wi-Fi).
- Tap the gear icon next to your active connection.
- Scroll to IP settings > change from "IPv6" to IPv4.
- Reconnect your VPN.
After disabling IPv6, test a website. If it loads, IPv6 was the culprit. You can re-enable it later if your VPN adds IPv6 support.
Try a Different Server or Server Location
A specific server can be overloaded, misconfigured, or blocked by your ISP. Switch to a different server in the same country first. If that fails, switch to a server in a neighboring country. On WireGuard, server load matters more because WireGuard uses a single IP per server. OpenVPN servers can handle more users. If you are on WireGuard and pages still fail after three server changes, switch to OpenVPN TCP on a server in a different region. Mullvad shows server load percentages in its app. Avoid servers above 70% load.
Flush Your DNS Cache and Reset Network Settings
Stale DNS entries from before your VPN connected can cause timeouts. Flush the cache and reset the network stack.
On Windows 11
- Open Command Prompt as Administrator.
- Type ipconfig /flushdns and press Enter.
- Then type ipconfig /release followed by ipconfig /renew.
- Finally, type netsh winsock reset and press Enter.
- Restart your computer.
On macOS Ventura
- Open Terminal.
- Type sudo dscacheutil -flushcache and press Enter.
- Type sudo killall -HUP mDNSResponder and press Enter.
- Restart your browser.
On Linux (Ubuntu 24.04 and similar)
- Open Terminal.
- Type sudo systemd-resolve --flush-caches and press Enter.
- Alternatively, type sudo resolvectl flush-caches.
- Restart your browser.
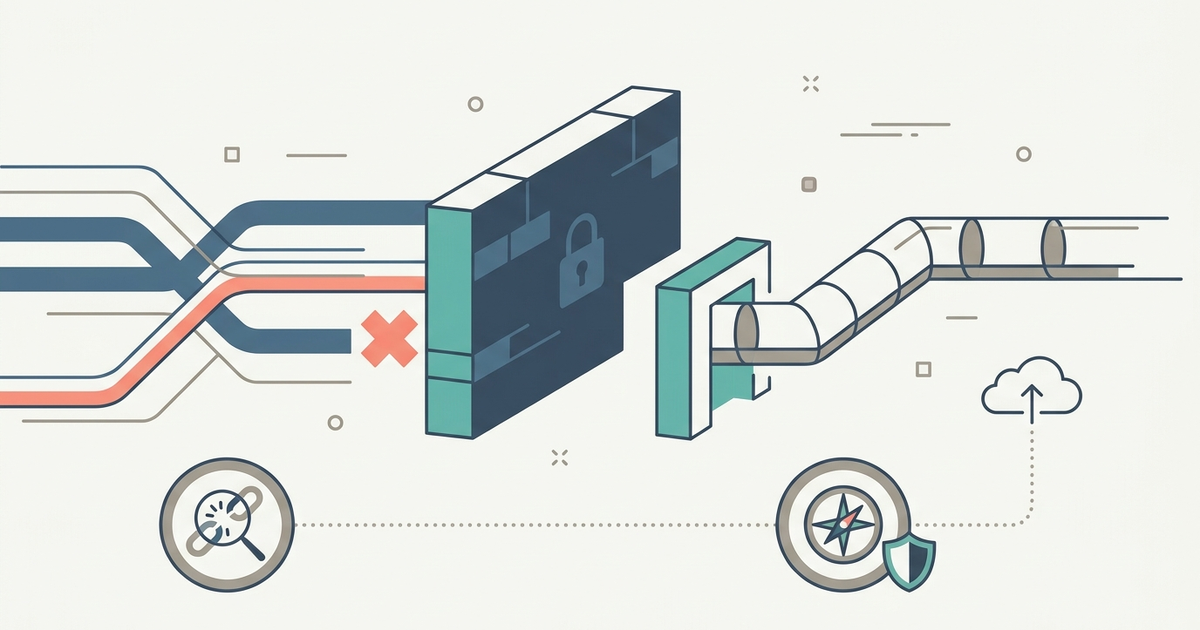
After flushing, reconnect your VPN and test a site. If it still fails, the problem is likely at the network level. Your ISP or firewall is actively blocking VPN traffic. Switch to OpenVPN TCP on port 443 or try a different VPN provider entirely. Mullvad and ExpressVPN both offer obfuscation features in their apps that make VPN traffic look like regular HTTPS. Enable obfuscation in the settings. That is the last tool in the box. If it works, you are done. If it does not, your network is blocking VPNs at a deeper level, and you may need a Shadowsocks or Tor bridge setup — but that is a separate article.
Part of our guide to How Network Blocks Work, and How To Get Around Them.